Welcome to awslagi.com – Sharing AWS, Google Cloud, Microsoft Azure IT Exams. It's free for all!

NSE7-SOC-AR-7-6: Fortinet NSE 7 - Security Operations 7.6 Architect

Master the Fortinet Fortinet NSE 7 - Security Operations 7.6 Architect (NSE7-SOC-AR-7-6) certification exam with 26 realistic practice questions covering SOAR Incident Handling and Threat Hunting, SOAR Playbook Development, SOC Concepts and Frameworks, Detection Capabilities.

4.8★★★★★(192 ratings)
15,376 studentsIntermediate
Prepare for the Fortinet Fortinet NSE 7 - Security Operations 7.6 Architect (NSE7-SOC-AR-7-6) certification with scenario-based practice questions modeled on real exam objectives. You will build practical confidence across key domains including SOAR Incident Handling and Threat Hunting, SOAR Playbook Development, SOC Concepts and Frameworks, Detection Capabilities. Each question includes structured answer options and hint answers to help you identify knowledge gaps quickly, reinforce core Fortinet concepts, and pass the NSE7-SOC-AR-7-6 exam on your first attempt.

What you'll learn

  • SOAR Incident Handling and Threat Hunting
  • SOAR Playbook Development
  • SOC Concepts and Frameworks
  • Detection Capabilities

NSE7-SOC-AR-7-6

Lectures1
Questions26
Duration30 week
Students15,376

$20.00

Full Free Question Bank (26 Questions)

NSE7-SOC-AR-7-6: Fortinet NSE 7 - Security Operations 7.6 Architect (NSE7-SOC-AR-7-6) Practice Questions & Verified Answers

Click any option to test your knowledge, or reveal the verified answer and detailed explanation below each question.

Question #1Part 1SOAR Incident Handling and Threat HuntingSelect 3

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1783916438251-1ofijkzw.png) You are attempting to find traffic flows to destinations in Europe or Asia for hosts in the local LAN segment. However, the query returns no results. Assume that these logs exist on FortiSIEM. Which three mistakes are present in the query shown in the exhibit? (Choose three.)
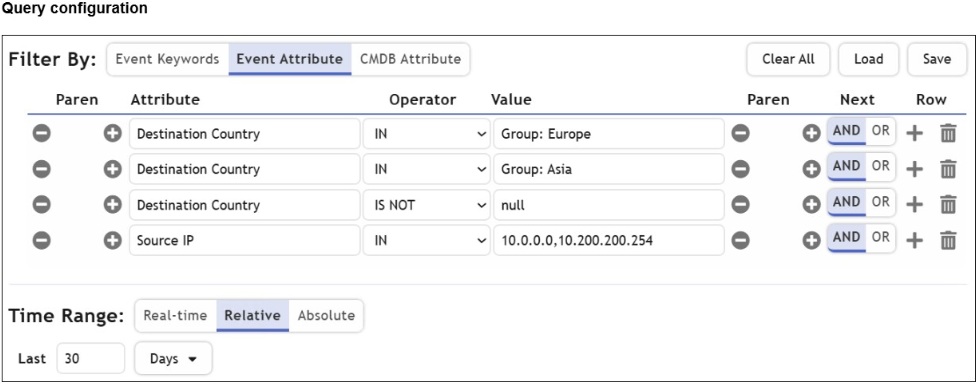
AThe logical operator for the first row (Group: Europe) must be OR.
BThe null value cannot be used with the IS NOT operator.
CThe time range must be Absolute for queries that use configuration management database (CMDB) groups.
DThe Source IP row operator must be BETWEEN 10.0.0.0, 10.200.200.254.
EThere are missing parentheses between the first row (Group: Europe) and the second row (Group: Asia).
Question #2Part 1SOAR Incident Handling and Threat Hunting

Which three of the following are threat-hunting activities?

AGenerate a hypothesis.
BTune correlation rules.
CPerform packet analysis.
DAutomate workflows.
EEnrich records with threat intelligence.
Question #3Part 1SOAR Playbook Development

When you configure an Ingest Bulk Feed playbook step, which two restrictions must be considered?

AIt will not trigger On Create triggers.
BIt is slower than the Create Record step.
CIt will not trigger On Update triggers.
DIt cannot use step output from a connector action.
Question #4Part 1SOC Concepts and Frameworks

Based on the Pyramid of Pain model, which two statements correctly describe an indicator’s value and the difficulty an adversary faces in changing it?

ATactics, techniques, and procedures are hard because adversaries must adapt their methods.
BTools are easy because often, multiple alternatives exist.
CIP addresses are easy because adversaries can spoof them or move them to new resources.
DArtifacts are easy because adversaries can alter file paths or registry keys.
Question #5Part 1Detection CapabilitiesSelect 2

You are setting up a new FortiSIEM rule to trigger incidents after receiving a specified number of either `Fortigate-Traffic-Violation` or `Fortigate-Traffic-Denied` event types. Although a single subpattern could accomplish this, you choose to create two separate subpatterns—one for each event type—and correlate them with the OR operator. Which two benefits does this method provide? (Choose two.)

AEach subpattern can use a different group by condition.
BEach subpattern can use a different time window condition.
CEach subpattern can use a different aggregate condition.
DEach subpattern can trigger its own notification policy.
Question #6Part 1SOAR Incident Handling and Threat HuntingSelect 2

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1783916432849-csbh652y.png) ![Question Image](https://cdn.examcademy.com/images/questions/1783916436483-zfze18h0.png) You configured the FortiSIEM connector in FortiSOAR. However, when attempting to save the configuration, you receive the error shown in the exhibit. What are two possible causes? (Choose two.)

AThe Visibility option must be set to Public.
BFortiSOAR cannot reach FortiSIEM.
CThe organization should be Super.
DThe user credentials do not match FortiSIEM.
Question #7Part 1SOC Concepts and FrameworksSelect 2

Review the incident report below. A fraudulent HR login page was emailed to several employees. The page replicated the company’s branding and captured usernames and passwords. The attacker subsequently used the stolen credentials to sign in through the company's web VPN portal. Which two MITRE ATT&CK tactics best characterize this report? (Choose two.)

ADefense Evasion
BCredential Access
CCommand and Control
DInitial Access
Question #8Part 1SOAR Incident Handling and Threat Hunting

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1783916615852-o2ndw7rz.png) You are investigating an open incident and want to add records from the custom Tickets module to the visual correlation widget. Assume that ticket records are already linked to the incident. How can you accomplish this?

AEdit the incident template and add the Tickets module to the graph.
BDefine move module relationships under Correlation Settings.
CTag ticket records with the incident ID.
DIngest ticket records through a custom connector.
Question #9Part 1SOAR Playbook Development

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1783916433621-33j7ey3p.png) A list of FortiSIEM connector actions is displayed. You want to build a FortiSOAR playbook that enables you to do the following: - Manually enter a range of IP addresses. - Use the connector action shown in the exhibit to retrieve, from the FortiSIEM configuration management database (CMDB), a list of devices in that IP-address range. - Create an asset record for each returned result, using the device IP address. Which combination and sequence of step operations meets these requirements with the fewest necessary playbook steps?

A1) Connector action, 2) Create record, 3) Update record
B1) On create trigger, 2) Connector action, 3) Code snippet, 4) Create record
C1) Manual trigger, 2) Connector action, 3) Create record
D1) Manual trigger, 2) Set variable, 3) Connector action, 4) Create record, 5) Update record
Question #10Part 1Detection Capabilities

You are using FortiSIEM analytics to refer to configuration management database (CMDB) event-type categories with these requirements: - Attribute: Event Type - Value: Group: Logon Success Which operator must be used for the analytics search?

AIN
BCONTAIN
CIS
DHAS
Question #11Part 1Detection CapabilitiesSelect 2

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1783916430417-wbe8elvj.png) Based on the configuration displayed, which two settings are misconfigured? (Choose two.)

AThe time window should be lowered from 900 seconds to reduce false positives.
BThe subpattern relationships between FailedLogin and FailedLogin2 should be removed.
CA logical operator is missing in the SuccessLogin subpattern to evaluate the subpattern relationships.
DThe SuccessLogin subpattern is not correlated with any FailedLogin or FailedLogin2 attributes.
Question #12Part 1SOC Concepts and Frameworks

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1783916621421-fpaa3f0y.png) Which approach most effectively reduces this organization's attack surface?

ARemove unused devices.
BEnable deep inspection on firewall policies.
CForward all firewall logs to the security information and event management (SIEM) system.
DImplement macrosegmentation.
Question #13Part 1Detection CapabilitiesSelect 2

You must create a nested query in FortiSIEM that meets these conditions: 1. Locate all devices discovered by any FortiSIEM Windows Agent. 2. From those devices, determine which have generated Windows Login Failure events. Which two query components should be used for this nested query? (Choose two.)

AOuter Event Query
BInner CMDB Query
COuter CMDB Query
DInner Event Query
Question #14Part 1SOC Concepts and Frameworks

Refer to the exhibit. A compromised PC creates an SSH connection to an engineering build server, which then relays HTTPS traffic to reach servers whose access from the LAN would otherwise be blocked. Which technique is used in this attack?

APort knocking
BExfiltration over C2 channel
CMan-in-the-middle (MITM)
DProtocol tunneling
Question #15Part 1SOAR Incident Handling and Threat Hunting

You created a war room and want to execute a connector action to check a domain’s reputation. You then need to save the output for your team to review, but the output is extensive and you want to restrict how much information is attached to the war room. How can you accomplish this?

AFrom the returned output, select only the output keys you want.
BUse the Investigate tab to map only the fields you want.
CLower the playbook logging level before executing the connector.
DApply a workspace filter to show only relevant fields.
Question #16Part 1SOAR Incident Handling and Threat Hunting

Which two phases belong to the FortiSOAR incident-handling process but are not phases in the NIST 800-61 Revision 2 model?

ADetection
BConfirmation
CIdentification
DPreparation
Question #17Part 1SOAR Incident Handling and Threat HuntingSelect 2

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1783923038505-ud9n5aq4.png) ![Question Image](https://cdn.examcademy.com/images/questions/1783923042184-a10xk5d8.png) You have configured the FortiGate connector on FortiSOAR. You want to permit FortiSOAR (10.200.200.160) to perform actions on FortiGate (172.16.200.1), but the connection attempt fails. Assume the FortiGate connector is configured correctly on the FortiSOAR side. Which two configurations are required on FortiGate? (Choose two.)

AHTTPS must be enabled on the FortiGate interface that FortiSOAR will communicate with.
BFortiSOAR IP address must be added under Trusted Hosts.
CThe administrator profile must have System read and write permissions.
DThe FortiGate interface role must be set to Custom API Endpoint.
Question #18Part 1SOAR Playbook DevelopmentSelect 2

You configured a new module named Users. Next, you want to set up a playbook that creates users from ingested data. When new records are created, you want to ensure duplicate users do not overwrite existing user records or their fields. However, you also want the playbook to keep running when duplicates are encountered so that any non-duplicate records are still created. Which two actions meet these requirements? (Choose two.)

AEnsure the Users module has record uniqueness conditions configured.
BConfigure the Execution Mode to run in parallel.
CUse the Do not create new record (keep existing intact) option in the Create Record step.
DUse the stop the create process option in the Create Record step.
Question #19Part 1SOAR Incident Handling and Threat Hunting

You want to use the queue and shift management feature to automatically assign newly created low-priority tasks to members of the L1 queue. However, you cannot add the Tasks module to the Module Types list. What is the issue?

AThe Tasks module is not supported by queue and shift management.
BThe Queueable option is disabled for the Tasks module.
CThere is a higher priority queue for the Tasks module.
DShift-based assignment is disabled.
Question #20Part 1SOAR Incident Handling and Threat Hunting

Refer to the exhibit. How can you add a piece of evidence to theAction Logs Marked As Evidencearea?

ABy creating an evidence collection task and attaching a file
BBy linking an indicator to the war room
CBy tagging output or a workspace comment with the keyword Evidence
DBy executing a playbook with the Save Execution Logs option enabled
Question #21Part 1SOAR Incident Handling and Threat Hunting

You configured a queue named L1 Analysts and created shifts covering morning, evening, and overnight periods, with two members assigned to each shift. However, you found that ingested alerts are assigned to every queue member in round-robin order rather than only to users who are currently on shift. What is the issue?

AThe shift lead needs to disable automatic shift handover.
BThe Queueable option is disabled for the alerts module.
CThe queue rules conflict with the user assignment rules.
DShift-based assignment is disabled.
Question #22Part 1SOAR Incident Handling and Threat Hunting

A partner organization recently had sensitive data exfiltrated by a well-known adversary group. You are tasked with threat hunting to determine whether your organization is also affected. Which action must you take first?

AUse threat intelligence to enrich the IP addresses of all destinations.
BReview the tactics, techniques, and procedures of the adversary.
CUse a packet analyzer to capture and review all traffic flows on critical devices.
DReview historical logs to establish a baseline for normal bandwidth usage.
Question #23Part 1SOAR Incident Handling and Threat HuntingSelect 2

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1783916428740-1r7gbj7l.png) You must configure the FortiGate connector so FortiSOAR can perform actions on a firewall. However, the connection fails. Which two configurations are required? (Choose two.)

ATrusted hosts must be enabled and the FortiSOAR IP address must be permitted.
BAn API administrator must be created on FortiGate with the appropriate profile, along with a generated API key to configure on the connector.
CThe VDOM name must be specified, or set to VDOM_1, if VDOMs are not enabled on FortiGate.
DHTTPS must be enabled on the FortiGate interface that FortiSOAR will communicate with.
Question #24Part 1Detection CapabilitiesSelect 2

Review the incident report. An attacker obtained employee names, roles, and email patterns from public press releases, then used them to create tailored emails. The emails instructed recipients to review an attached agenda through a link hosted outside the corporate domain. Which two MITRE ATT&CK tactics most closely match this report? (Choose two.)

ADiscovery
BInitial Access
CDefense Evasion
DReconnaissance
Question #25Part 1SOAR Playbook Development

Which three capabilities does the built-in FortiSOAR Jinja editor provide?

AIt renders output by combining Jinja expressions and JSON input.
BIt checks the validity of a Jinja expression.
CIt loads the environment JSON of a recently executed playbook.
DIt defines conditions to trigger a playbook step.
EIt creates new records in bulk.
Question #26Part 1Detection Capabilities

Refer to the following partial incident output: What conclusion can you draw about this incident?

AIt was triggered by a lookup table.
BIt was triggered by a correlation rule.
CIt was triggered by a baseline profile incident rule.
DIt was triggered from a FortiAI machine learning rule.

📢 Unlock Full Access to Success!

"The content displayed here is a promotional preview and contains only 50% of the actual exam database. To access the complete set of updated questions, please upgrade to the Full Version."

👉 Click the button and follow the instructions to secure your full access immediately!