Welcome to awslagi.com – Sharing AWS, Google Cloud, Microsoft Azure IT Exams. It's free for all!

NSE6-SDW-AD-7-6: Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator

Master the Fortinet Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator (NSE6-SDW-AD-7-6) certification exam with 31 realistic practice questions covering Advanced IPsec, Centralized management, Rules and routing, SD-WAN troubleshooting.

4.8★★★★★(248 ratings)
19,692 studentsIntermediate
Prepare for the Fortinet Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator (NSE6-SDW-AD-7-6) certification with scenario-based practice questions modeled on real exam objectives. You will build practical confidence across key domains including Advanced IPsec, Centralized management, Rules and routing, SD-WAN troubleshooting. Each question includes structured answer options and hint answers to help you identify knowledge gaps quickly, reinforce core Fortinet concepts, and pass the NSE6-SDW-AD-7-6 exam on your first attempt.

What you'll learn

  • Advanced IPsec
  • Centralized management
  • Rules and routing
  • SD-WAN troubleshooting
  • SD-WAN setup

NSE6-SDW-AD-7-6

Lectures1
Questions31
Duration30 week
Students19,692

$20.00

Full Free Question Bank (31 Questions)

NSE6-SDW-AD-7-6: Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator (NSE6-SDW-AD-7-6) Practice Questions & Verified Answers

Click any option to test your knowledge, or reveal the verified answer and detailed explanation below each question.

Question #1Part 1Advanced IPsec

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784226774507-ict4ppbz.png) Which statement accurately describes the ADVPN device’s role when handling this traffic?
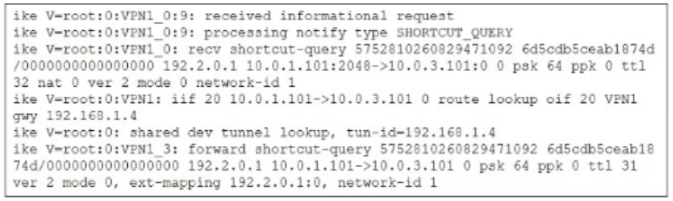
AThis device is a spoke that has received a shortcut query from another spoke and has forwarded the response to its hub.
BThis device is a hub that has received a query from a spoke and has forwarded it to another spoke.
CThis device is a hub in a dual-region topology and the remote hub tunnel ID is 10.0.2.101.
DThis device is a spoke and the kernel received a shortcut request and forwards the query to another spoke.
Question #2Part 1Centralized managementSelect 2

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784226768537-ybj9hxnx.png) For your ZTP deployment, you review the CSV file displayed in the exhibit and notice that it lacks important information. Which two elements must you change before importing it into FortManager? (Choose two.)

AYou must define a name for each device
BYou must define a value for each device and each user-defined motadata variable.
CYou must associate a device blueprint with each device.
DYou must define a value for each device and each metadata variable that defines an IP address.
Question #3Part 1Rules and routing

In what sequence does FortiGate evaluate the following elements during route lookup?

ASD-WAN rules, ISDB routes, policy routes, BGP routes
BSD-WAN rules, policy routes, static routes, ISDB routes
CPolicy routes, ISDB routes, SD-WAN rules, static routes
DPolicy routes, SD-WAN rules, Internet Service Database (ISDB) routes, BGP routes
Question #4Part 1Advanced IPsec

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784142772524-vltp34w4.png) You used the SD-WAN overlay orchestrator to prepare an IPsec tunnel configuration for a hub-and-spoke SD-WAN topology. The exhibit displays the FortiManager installation preview for one FortiGate device. Based on the exhibit, which statement accurately describes the configuration applied to the FortiGate device?

AIt is a hub device. It will automatically discover the spoke devices and add them to the SD-WAN topology.
BIt is a spoke device that establishes dynamic IPsec tunnels to the hub. The local subnet range is 10.10.128.0/23.
CIt is a hub device. It can send ADVPN shortcut offers.
DIt is a spoke device that establishes dynamic IPsec tunnels to the hub. It can send auto-discovery VPN (ADVPN) shortcut requests.
Question #5Part 1Rules and routing

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784226762432-n585octh.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226766649-hu8pehfp.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226770656-pzopoov0.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226773487-5c1nwi3s.png) You collected the outputs displayed in the exhibits and need to determine which interface HTTP traffic from user device `10.0.1.101` to the corporate web server `10.0.0.126` will traverse. All SD-WAN links are stable. Which interface will FortiGate use to steer the traffic?

AEither HUB1-VPN1, HUB1-VPN2, or HUB1-VPN3
BOnly HUB1-VPN3
COnly HUB1-VPN2
DEither HUB1-VPN2 or HUB1-VPN3
Question #6Part 1SD-WAN troubleshooting

Refer to the exhibit showing `diagnose` output from a FortiGate device. ![Question Image](https://cdn.examcademy.com/images/questions/1784226686673-dnb2tf78.png) Based on the output displayed in the exhibit, what can you conclude about the device role and its handling of health checks?

AThe device is a spoke and it provides embedded health-check measures for each tunnel to the hub.
BThe device is a spoke and it receives health-check measures for the tunnels of another spoke.
CThe device is a hub and it receives embedded health-check measures for each tunnel from the spoke.
DThe device is a hub and it receives health-check measures for the tunnels of a spoke.
Question #7Part 1SD-WAN setupSelect 2

When deploying SD-WAN, you can select from several common designs. Each design is best suited to particular contexts. Which two statements correctly match a common SD-WAN design to its primary indication or constraint? (Choose two.)

AUse a standalone design for sites with only one WAN link to the cloud.
BUse a cloud on-ramp topology to improve the performance of cloud applications.
CUse a direct internet access (DIA) design to increase the traffic security and allow local devices with limited capabilities.
DUse remote breakout to centralize traffic inspection and limit local management requirements.
Question #8Part 1SD-WAN setupSelect 2

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784226761807-46cdm0qe.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226764716-7w1kbmyf.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226768291-z4e192zr.png) Which two statements are correct about the health and performance of SD-WAN members 3 and 4? (Choose two.)

AEncrypted traffic is not used for the performance measurement
BOnly related TCP traffic is used for performance measurement.
CFortiGate identifies the member as dead when there is no Facebook and YouTube traffic passing through the member.
DThe performance is an average of the metrics measured for Facebook and YouTube traffic passing through the member.
Question #9Part 1Rules and routing

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784226690195-jdrnqgdm.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226693699-vppcierg.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226697080-pkf37tkd.png) You use FortiManager to configure SD-WAN across three branch devices. When installing the device settings, FortiManager displays the error **“Copy Failed”** for device `branch1_fgt`. After clicking the log button, FortiManager shows the message in the exhibit. Based on the exhibits, which statement best describes the issue and how it can be resolved?

ACheck the metadata variable definitions, and review the per-device mapping configuration.
BRemove the installation target for the SD-WAN member port4. You cannot combine metadata variable and installation targets.
CGateways for all members in a zone must be defined the same way. Specify the gateway of the SD-WAN member port1 without metadata variables.
DCheck the connection between branch1_fgt and FortiManager.
Question #10Part 1Centralized managementSelect 2

As an IT manager, you need to delegate installation and management of your SD-WAN deployment to a managed security service provider (MSSP). Each site must retain direct Internet access and remain secure. You anticipate substantial traffic between the sites and want to delegate as much network administration and management as possible to the MSSP. Which two MSSP deployment blueprints meet these requirements? (Choose two.)

AInstall the hub and spokes on the customer premises, and enable the MSSP to manage the SD-WAN deployment using FortiManager with a dedicated ADOM.
BUse a shared hub on the MSSP premises and a dedicated hub on the customer premises, and install the spokes on the customer premises.
CInstall a dedicated hub on the MSSP premises for the customer, and install the spokes on the customer premises.
DUse a shared hub on the MSSP premises with a dedicated VDOM for the customer, and install the spokes on the customer premises.
Question #11Part 1Rules and routing

Refer to the exhibit. Which SD-WAN rule and interface does FortiGate use to steer traffic from LAN subnet 10.0.1.0/24 to the corporate server 10.2.5.254?

ASD-WAN service rule 3 and interface HUB1-VPN2.
BSD-WAN service rule 4 and port1 or port2.
CSD-WAN service rule 3 and interface HUB1-VPN3.
DSD-WAN service rule 4 and interface port2.
Question #12Part 1SD-WAN troubleshooting

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784142538091-rhhgo7hd.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784142541256-w3maod98.png) The SD-WAN rule configuration, along with its corresponding rule status and routing table, is displayed. You want to determine the expected behavior for traffic matching the SD-WAN rule at the time the output was captured. Based on the exhibits, which behavior should you expect for traffic that matches the SD-WAN rule?

AThe traffic will be routed over HUB1-VPN1.
BThe traffic will be load balanced across all three overlays.
CThe traffic will be routed over HUB1-VPN2.
DThe traffic will be routed over HUB1-VPN3.
Question #13Part 1SD-WAN setupSelect 3

You use the FortiManager SD-WAN overlay orchestrator to prepare an SD-WAN deployment. Based on the information supplied through the SD-WAN overlay template wizard, FortiManager generates templates that are ready to install on the spoke and hub devices. Which three templates does the SD-WAN overlay orchestrator create for a spoke device? (Choose three.)

ACLI template
BBGP template
CRules template
DStatic route template
EIPsec tunnel template
Question #14Part 1SD-WAN troubleshooting

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784226760536-bf2rkrdk.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226764191-j1d1uvzo.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226767365-gpnrjxke.png) You use FortiManager to manage the branch devices and configure the SD-WAN template. You update the configuration to meet new user requirements and configure the firewall policies shown in the second exhibit. When you then use the Install Wizard to install the updated configuration and firewall policy package on the branch devices, FortiManager reports the error shown in the third exhibit. Why is FortiManager unable to install the configuration on the branch devices?

AYou must direct traffic with the default security profile to a VPN tunnel.
BYou cannot install firewall policies that reference an SD-WAN member.
CYou cannot install firewall policies that reference an SD-WAN zone.
DYou cannot install firewall policies for HTTPS traffic with no SSL inspection.
Question #15Part 1SD-WAN troubleshootingSelect 2

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784142541290-t5r5wtg3.png) Which two conclusions are supported by the displayed output? (Choose two.)

AUDP traffic destined to the subnet 10.22.0.0/24 matches a policy route.
BAt least one SD-WAN rule is defined with application categories as the destination.
CAt least one SD-WAN rule allows traffic load balancing.
DUDP traffic destined to the subnet 10.22.0.0/24 matches a manual SD-WAN rule.
Question #16Part 1SD-WAN setup

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784142747231-e9g2d6dh.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784142749827-l03fhv79.png) How does FortiGate process traffic with source IP address 10.0.1.125 and destination IP address 128.66.0.125?

AFortiGate routes the traffic flow according to the forwarding information base (FIB).
BFortiGate steers the traffic flow through port7.
CFortiGate load balances the traffic flow through port7 and port8.
DFortiGate drops the traffic flow.
Question #17Part 1Centralized management

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784226760887-1xjxeffe.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226763915-3vhfm97e.png) The SD-WAN zone configuration for an SD-WAN template created on FortiManager and the policy package configuration are displayed. When attempting to install the configuration changes, FortiManager shows an error message. How can the issue be resolved?

AConfigure a normalized interface for the IPsec tunnel HUB1-VPN1.
BConfigure both HUB1-VPN1 and HUB1-VPN2 as the destination of policy 3.
CConfigure HUB1 as the destination of policy 3.
DConfigure branch1_fgt as the installation target for policy 3.
Question #18Part 1Centralized managementSelect 3

Which three characteristics apply to the provisioning templates available on FortiManager? (Choose three.)

AA CLI template can be of type CLI script or Perl script.
BA CLI template group can contain CLI templates of different types.
CCLI templates are applied in order, from top to bottom.
DEach template group can contain up to three IPsec tunnel templates.
EA template group can include a system template and an SD-WAN template.
Question #19Part 1SD-WAN troubleshootingSelect 2

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784226687471-mkotu051.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784226690899-bslsqsgo.png) An administrator is testing application steering in SD-WAN. Before generating test traffic, the administrator gathered the information shown in the first exhibit. After generating GoToMeeting test traffic, the administrator reviewed the related traffic log on FortiAnalyzer, shown in the second exhibit. The administrator observed that the traffic matched the implicit SD-WAN rule, although they expected it to match rule ID 1. Which two reasons explain why some log messages indicate that the traffic matched the implicit SD-WAN rule? (Choose two.)

ANo configured SD-WAN rule matches the traffic related to the collaboration application GoToMeeting.
BFull SSL inspection is not enabled on the matching firewall policy.
CThe session 3-tuple did not match any of the existing entries in the ISDB application cache.
DFortiGate could not refresh the routing information on the session after the application was detected.
Question #20Part 1SD-WAN setup

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784142758286-rfjevdr3.png) You plan to configure SD-WAN on a network, as illustrated in the exhibit. The network includes many FortiGate devices. Some operate as next-generation firewalls (NGFW), while others have extensions installed, such as FortiSwitch, FortiAP, or FortiExtender. Which factors should you consider when planning the deployment?

AYou can build an SD-WAN topology that includes all devices. The hubs must be devices without extensions.
BYou should build multiple SD-WAN topologies. Each topology should contain only one type of extension.
CYou can build an SD-WAN topology that includes all devices. The hubs can be FortiGate devices with FortiExtender.
DYou should exclude the FortiGate devices with FortiLink connection from the SD-WAN topology.
Question #21Part 1Rules and routing

Refer to the exhibit. An administrator configured two SD-WAN rules for traffic load balancing. Which interfaces does FortiGate use to steer traffic from 10.0.1.124 to 10.0.0.254?

AAny interface in the HUB1 or HUB2 zones.
BHUB1-VPN2
Cpor1 or port2
DFortiGate route the traffic according to the FIB.
Question #22Part 1SD-WAN troubleshooting

Refer to the exhibit. An event log on a FortiGate device is displayed. Based on the output displayed in the exhibit, what can you conclude about the tunnels on this device?

AThe master tunnel HUB2-VPN3 cannot accept auto-discovery VPN (ADVPN) shortcuts.
BThe voice traffic is steered through the VPN tunnel HUB1-VPN3.
CThere is one shortcut tunnel built from the master tunnel VPN4.
DThe VPN tunnel HUB1-VPN1_0 is a shortcut tunnel.
Question #23Part 1SD-WAN setupSelect 2

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784142769030-xfcj6ai1.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784142771744-thptsh8i.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784142774474-gigb4fxj.png) The administrator raises the member priority on port2 to 20. Assuming that the route exiting port2 remains valid, after the configuration changes and when new packets are received, which two actions does FortiGate take for existing sessions established through port2? (Choose two.)

AFortiGate updates the gateway information of the sessions with SNAT so that they use port1 instead of port2.
BFortiGate continues routing all existing sessions over port2.
CFortiGate flags all source network address translation (SNAT) sessions as dirty only if the administrator has assigned an IP pool to the firewall policies with NAT.
DFortiGate routes new sessions over port1.
EFortiGate flags all sessions as dirty.
Question #24Part 1SD-WAN troubleshootingSelect 2

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784142754338-cwochmt2.png) The health-check configuration displayed is for a FortiGate device operating as a spoke. The hub FortiGate is not prioritizing traffic as expected. Which two configuration elements should be checked on the hub? (Choose two.)

AThe performance SLA uses the same members.
BThe performance SLA uses the same criteria.
CThe performance SLA is configured with set embedded-measure accept.
DThe performance SLA has the parameter priority-out-sla configured.
Question #25Part 1Rules and routing

You are planning a large SD-WAN deployment for a global company. You want to split the network architecture into five geographic regions and deploy two hubs in each region for greater redundancy. You anticipate substantial traffic within every region and limited traffic between spokes in separate regions. You plan to connect small branch sites only to the nearest hub in their respective regions, while connecting large branch sites to both hubs in their regions. Which statement about this plan is true?

AIt is possible. You should use FortiManager and the overlay orchestrator multihub topology to simplify the deployment.
BIt is not possible. In a region, all spokes must have either single-hub or dual-hub connectivity.
CIt is possible. You should use EBGP as the routing protocol between the regions.
DIt is not possible. FortiOS 7.6 supports multihub topologies with up to four hubs.
Question #26Part 1SD-WAN setup

Refer to the exhibits. ![Question Image](https://cdn.examcademy.com/images/questions/1784142759554-qg1ynk4g.png) ![Question Image](https://cdn.examcademy.com/images/questions/1784142763382-ivvbo0lg.png) The SD-WAN zone and member configurations for two branch devices are displayed. The two branch devices belong to the same hub-and-spoke topology and connect to the same hub. They are configured to permit Auto Discovery VPN (ADVPN), and the hub configuration permits the initial communication between the two spokes. When traffic flow requires it, between which interfaces can the devices establish shortcuts?

AAny interface in the overlay zones
BInterface connected to HUB only.
CBetween T2 on Branch-A and TA on Branch-B
DBetween T3 on Branch-A and TC on Branch-B
Question #27Part 1SD-WAN troubleshooting

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784142775430-t49zx8ij.png) Which action does FortiGate take when it detects the SD-WAN members as dead?

AFortiGate bounces port5 after it detects all SD-WAN members as dead.
BFortiGate brings down port5 after it detects all SD-WAN members as dead.
CFortiGate sends alert messages through port5 when it detects all SD-WAN members as dead.
DFortiGate fails over to the secondary device after it detects port5 as dead.
Question #28Part 1Advanced IPsecSelect 2

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784226693708-zyfh93r9.png) Two hub-and-spoke groups are linked through redundant site-to-site IPsec VPNs between Hub 1 and Hub 2. Which two configuration settings are necessary for spoke A1 to establish an ADVPN shortcut with spoke B2? (Choose two.)

AOn hubs, auto-discovery-receiver must be enabled on the IPsec VPNs to spokes.
BOn hubs, auto-discovery-forwarder must be enabled on the IPsec VPNs to spokes.
COn hubs, auto-discovery-forwarder must be enabled on the IPsec VPNs to hubs.
DOn hubs, auto-discovery-sender must be enabled on the IPsec VPNs to spokes.
Question #29Part 1SD-WAN troubleshootingSelect 2

Refer to the exhibit. ![Question Image](https://cdn.examcademy.com/images/questions/1784226771613-6tkj1odr.png) You are using the FortiManager SD-WAN monitor menus to check an SD-WAN topology’s status. When you hover the mouse next to `branch1_fgt`, you receive the output shown in the exhibit. Which two conclusions can be drawn from the output shown in the exhibit? (Choose two.)

Abranch1_fgt is configured with six SD-WAN overlay tunnels and three are down.
BThe three spokes have tunnels that are out of SLA.
CThe template Corp-SOT defines a dual-hub topology.
Dbranch3_fgt is configured with three SD-WAN overlay tunnels and one is down.
Question #30Part 1Rules and routing

You are planning a new SD-WAN deployment with these criteria: - Two regions - Most traffic is expected to stay within its region - No inter-region ADVPN is required To follow recommended best practices, which routing protocol should you choose for the overlays?

AOSPF for the routing within each region and EBGP between the regions.
BIBGP within each region and between the regions.
CIBGP with BGP per overlays within each region and IBGP with BGP on loopback between the regions.
DIBGP with BGP on loopback within each region and EBGP between the regions.
Question #31Part 1SD-WAN setupSelect 2

In SD-WAN, the terms *underlay* and *overlay* are commonly used to classify links. Which two statements about underlay and overlay links are correct? (Choose two.)

AOverlay links provide routing flexibility.
BFortiLink interface is considered an underlay link.
CA VLAN is a type of overlay link.
DOnly wired connections can be used as underlay links.
EWireless connections can be used to build overlay links.

📢 Unlock Full Access to Success!

"The content displayed here is a promotional preview and contains only 50% of the actual exam database. To access the complete set of updated questions, please upgrade to the Full Version."

👉 Click the button and follow the instructions to secure your full access immediately!