Welcome to awslagi.com – Sharing AWS, Google Cloud, Microsoft Azure IT Exams. It's free for all!

CCFH-202B: CrowdStrike Certified Falcon Hunter

Master the CrowdStrike CrowdStrike Certified Falcon Hunter (CCFH-202B) certification exam with 46 realistic practice questions covering Event Search, Detection Analysis, Search and Investigation Tools, Hunting Methodology.

4.8★★★★★(253 ratings)
20,345 studentsIntermediate
Prepare for the CrowdStrike CrowdStrike Certified Falcon Hunter (CCFH-202B) certification with scenario-based practice questions modeled on real exam objectives. You will build practical confidence across key domains including Event Search, Detection Analysis, Search and Investigation Tools, Hunting Methodology. Each question includes structured answer options and hint answers to help you identify knowledge gaps quickly, reinforce core CrowdStrike concepts, and pass the CCFH-202B exam on your first attempt.

What you'll learn

  • Event Search
  • Detection Analysis
  • Search and Investigation Tools
  • Hunting Methodology
  • ATT&CK Frameworks
  • Reports and References

CCFH-202B

Lectures1
Questions46
Duration30 week
Students20,345

$20.00

Full Free Question Bank (46 Questions)

CCFH-202B: CrowdStrike Certified Falcon Hunter (CCFH-202B) Practice Questions & Verified Answers

Click any option to test your knowledge, or reveal the verified answer and detailed explanation below each question.

Question #1Part 1Event Search

Refer to the image. ![Question Image](https://cdn.examcademy.com/images/questions/1784139139447-s8tj1b4z.png) Why are there six pending-containment events?
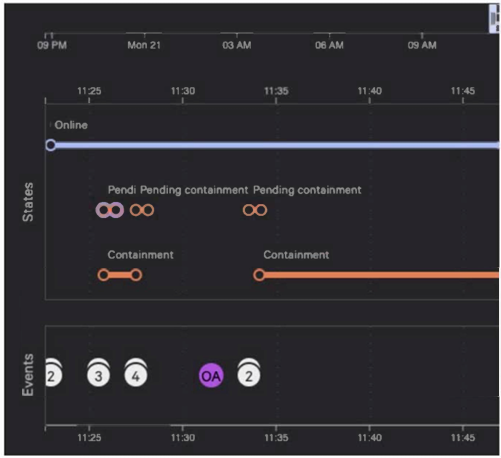
AWhen requesting containment of a device, there is one event to contain the host by Agent ID, and another event to contain by Mac Address
BWhen requesting containment of a device, there is one event for the change request, and another corresponding to the completed status of the request
CWhen requesting containment of a device, there is one event for checking of the current host state, and another corresponding to the change request0
DWhen requesting containment of a device, there is one event to contain the host by Agent ID, and another event to contain by Host Name
Question #2Part 1Event Search

You are investigating several `NetworkConnectIP4` events, all with the same `ContextProcessId` of `123456789`. Which query will display the process responsible for these `NetworkConnectIP4` events?

A#event_simpleName-ProcessRollup2 or #event_simpleName-SyntheticProcessRollup2 TargetProcessId = 123456789
B#event_simpleName=ProcessRollup2 or #event_simpleName=SyntheticProcessRollup2 ParentProcessId = 123456789
C#event_simpleName-ProcessRollup2 or #event_simpleName-SyntheticProcessRollup2 RpcProcessId = 123456789
D#event_simpleName=ProcessRollup2 or #event_simpleName=SyntheticProcessRollup2 RawProcessId = 123456789
Question #3Part 1Event Search

Falcon is producing detections for a malicious file, `evil.exe`, across several hosts and varying file paths as end users try to run it. Which query can proactively hunt for locations where the file exists before a user executes it?

A![](https://cdn.examcademy.com/images/questions/1785604112484-iyhcgewh.png)
B![](https://cdn.examcademy.com/images/questions/1785604118238-piymwon6.png)
C![](https://cdn.examcademy.com/images/questions/1785604120826-2v47y3mp.png)
D![](https://cdn.examcademy.com/images/questions/1785604123161-3cty2ffk.png)
Question #4Part 1Event Search

You have created an Advanced Event Search query to identify suspicious PowerShell usage and want to show its results on a dashboard. How can you display this query in a dashboard?

ACreate a scheduled workflow to execute the query
BSave the query as a saved search
CSave the query as a dashboard widget
DConfigure a scheduled search with the query
Question #5Part 1Event Search

Which statement filters all events associated with a new scheduled task registered by the user "Doris"?

A#event_simpleName=NewScheduledTaskRegistered | UserName="Doris"
B#event_simpleName=ProcessRollup2 FileName="*.sht" | UserName="Doris"
C#event_simpleName=ProcessRollup2 ProcessName="taskmgr.exe" | UserName="Doris"
D#event_simpleName=ScheduledTaskRegistered | UserName="Doris"
Question #6Part 1Detection Analysis

An alert is received for this process tree: IIS/W3WP.exe -> Powershell.exe -> cmd.exe -> whoami.exe -> net1.exe Which of the following describes what has happened?

AEmail gateway validating user permissions with whoami and network status with net1
BReconnaissance commands run via a Webserver compromise
CWebserver troubleshooting user access issues by querying whoami and net1
DEmail gateway automating routine tasks for whoami and net1 networking configuration
Question #7Part 1Search and Investigation Tools

What is one method for creating a new dashboard widget?

ASave a search query to automatically create the widget
BImport results from a scheduled search as a widget
CSave an Advanced Event Search as a widget
DCreate through scheduled searches based on correlation rules
Question #8Part 1Hunting Methodology

You receive several automated detections of a script named `1.ps1` executing across several different endpoints. What action should you take first to determine whether the script is malicious?

AReview ScriptControl events to identify the content of the script
BImmediately contain the device and remove the file from disk
CReview all machine learning detections on the device to determine if the script matched a signature scan
DContact the end user of the devices where the script was executed and ask them if it was approved activity
Question #9Part 1Hunting Methodology

A ransomware infection has spread across the enterprise. What would be the first action you take to determine the infection source?

AUtilize Falcon Investigate to find patient zero and search for initial infection activity
BPerform reverse engineering on the malware sample to see if you can find the infection vector
CPerform a vulnerability assessment to see what vulnerability could've been exploited
DSpeak with users to see what workstation was the first to be encrypted
Question #10Part 1Detection Analysis

Refer to the image. Which line item in the query is used to perform outlier analysis?

ALine 2
BLine 3
CLine 4
DLine 6
Question #11Part 1Hunting Methodology

While hunting for unusual PowerShell commands, you find the following command running on one host: `powershell.exe "(New-Object Net.WebClient).DownloadString('https://raw.githubusercontent.com/.../Invoke-AppPathBypass.ps1')"` The process tree for this command is: `winlogon.exe > userinit.exe > explorer.exe > powershell_ise.exe > powershell.exe` All commands ran during normal working hours under an IT department user's account. What should your next investigation steps be?

ANetwork contain the host and prepare the machine for a full re-image
BStart an RTR session on the host. Check the user's Downloads folder for the file AppPathBypass.ps1 and delete the file
CMark the detection as True Positive. Trigger an automated remediation to remove all malicious files and methods of persistence
DPerform a +/- 10 minute search for events around this process execution to get more context. Contact the user to confirm whether or not this was testing-related activity
Question #12Part 1ATT&CK Frameworks

A compromised host contains evidence that the commandnet user hacker password123 /add /domainwas run. Which MITRE ATT&CK technique does this correspond to?

AExecution
BPrivilege Escalation
CDefense Evasion
DPersistence
Question #13Part 1Detection Analysis

Which scenario is an appropriate use of thejoin()function in a query?

AWhen you need to join the same query from different time frames
BWhen you have two queries with a common value that need to be combined
CWhen you have two queries that may contain correlated information that you want to combine
DWhen you want to combine two queries to generate additional fields
Question #14Part 1ATT&CK Frameworks

An attacker creates a scheduled task that runs a remote management application. Which stage of the MITRE ATT&CK Matrix for Enterprise does this illustrate?

ALateral Movement
BPrivilege Escalation
CGaining Access
DPersistence
Question #15Part 1Event Search

When investigating two related processes in Advanced Event Search, how does `ContextProcessId` relate to `TargetProcessId`?

AWhen Process 1 spawns, it has a TargetProcessId and matches the ContextProcessId of Process 1 for a different process chain
BWhen Process 1 spawns Process 2, the ContextProcessId of Process 1 will match the TargetProcessId of Process 2
CWhen Process 1 spawns Process 2, the TargetProcessId of Process 1 will match the ContextProcessId of Process 2
DWhen Process 1 spawns, it has a ContextProcessId and matches the TargetProcessId of Process 1 for a different process chain
Question #16Part 1Event Search

Which query returns every process execution for the fileEXCEL.EXE?

A#event_simpleName=ProcessRollup2 ImageFileName=EXCEL.EXE
B#event_simpleName=ProcessRollup2 CommandLine=EXCEL.EXE*
C#event_simpleName=ProcessRollup2 FileName=EXCEL.EXE
Question #17Part 1Detection Analysis

While triaging a detection, you observe an event namedSyntheticProcessRollup2. What conclusion can be drawn about this event?

AThe event was generated for a process which is not built-in to the host's Operating System
BThe event was generated for a process which started before the sensor did
CThe event was generated to provide context on process injection techniques being used on the host
DThe event was generated as a result of a critical detection
Question #18Part 1Hunting Methodology

You observe an unusual spike in PsExec usage across multiple machines in your environment. Which action will confirm whether this activity is legitimate or malicious?

AContain the host until you can perform an investigation of the PowerShell commands
BVerify if the commands were run by an authorized administrator account performing known legitimate activity
CFlag the user to monitor for further activity
Question #19Part 1Search and Investigation Tools

You are investigating detections involving network reconnaissance, including several commands run by `cmd.exe`, and need to determine the root cause. How can you rapidly verify whether these commands resulted from an exploited vulnerability?

ACheck the process tree and all parent processes to see how cmd.exe was launched
BContain the host and see if more commands are being issued by this process
CCompare the utilized commands in cmd.exe to other commands used by admins of this organization
Question #20Part 1Reports and References

While conducting an investigation, you find a Falcon host connecting from a country outside those in which you normally conduct business. Which built-in report shows Falcon hosts connecting from that country?

AGlobal connection heat map
BGeo location activity
CRemote access graph
DAttack Paths
Question #21Part 1Hunting Methodology

Your organization relies on an internally developed application for operations. The application is generating Indicators of Attack (IOA) detections for vulnerable-driver use on servers where Falcon was recently installed. After reviewing the application, you determine that its behavior is expected. What will reduce risk in the environment the most?

ACreate an IOA exclusion for this activity
BCreate a Machine Learning Exclusion
CCreate a Sensor Visibility Exclusion
DUpdate the vulnerable driver to a non-vulnerable recent version
Question #22Part 1Hunting Methodology

A ransomware infection has spread across the enterprise. What first action would you take to identify the source of the infection?

APerform reverse engineering on the malware sample to see if you can find the infection vector
BUtilize Exposure Management to identify systems with critical vulnerabilities that could be exploited
CPerform a PowerShell hunt to look for suspicious PowerShell commands
DUse Advanced Event Search to timeline encryption activity and determine the system with the first encryption event
Question #23Part 1Search and Investigation Tools

Which CQL query would return relevant data for tracking USB storage-device usage?

AB.
CD.
Question #24Part 1Search and Investigation Tools

You have received a detection and want to start analyzing the triggering file in the Process Timeline dashboard. What is required to run the search?

AContextProcessId
BCompany
CTargetProcessId
D#event_simpleName
Question #25Part 1Search and Investigation Tools

Which CQL function is recommended for exporting a few fields from a large number of events (>100,000) to a CSV file?

Acollect()
Bselect()
Ctable()
DoutputCsv()
Question #26Part 1Event Search

An independent investigation team in Europe requests that Event Search data be formatted in Central European Summer Time. Which parameter in theformatTime()function is required to convert the Unix timestamps?

Atimezone
Bunit
Clocale
Dformat
Question #27Part 1Detection Analysis

A detection contains the following command line: ```text C:\Windows\system32\cmd.exe /Q /c echo ping -n 1 google.com ^> \\VICTIM-MACHINE\C$\__output 2^>^&1 > C:\Windows\pJYOrvQB.bat & C:\Windows\system32\cmd.exe /Q /c C:\Windows\pJYOrvQB.bat &del C:\Windows\pJYOrvQB.bat ``` What activity does this describe? C:\Windows\system32\cmd.exe /Q /c echo ping -n 1 google.com ^> \\VICTIM-MACHINE\C$\__output 2^>^&1 > C:\Windows\pJYOrvQB.bat & C:\Windows\system32\cmd.exe /Q /c C:\Windows\pJYOrvQB.bat &del C:\Windows\pJYOrvQB.bat

AAdministrator testing network activity via connectivity of .bat script to ping google.com
BAdministrator setting default DNS resolver for google.com via a .bat script
CImpacket tooling executing Mimikatz attack via a .bat script as a part of privilege escalation activity
DImpacket tooling testing network connectivity on host as a part of reconnaissance activity
Question #28Part 1Event Search

Which query can be used to filter users with more than 25 total logons?

A#event_simpleName=UserLogon| stats(UserName)| where (totalLogons >25)
B#event_simpleName=UserLogon| groupBy(UserName, function=(count(aid, as=totalLogons)))| test(totalLogons > 25)
C#event_simpleName=UserLogonI stats(UserName, function=(count(aid, as=totalLogons)))| where(totalLogons > 25)
D#event_simpleName=UserLogon| groupBy(UserName)| where(totalLogons >25)
Question #29Part 1Detection Analysis

An alert is received for the following process tree: Outlook.exe → iexplore.exe → Winword.exe → cmd.exe → PowerShell.exe What occurred based on the information provided?

AA user selected Open with Outlook on a Word file, which utilizes PowerShell to initiate this process
BA user executed a malicious PowerShell command which used cmd to send a malicious Word document using Outlook
CA user initiated a software update of Outlook, which used Internet Explorer to download a Word document, that then used cmd.exe and PowerShell to install malware
DA user received an email in Outlook with a malicious link to download a trojanized Word document containing a malicious macro
Question #30Part 1Reports and References

Which built-in hunting report helps identify executables running from the Recycle Bin?

ADetection Activity
BCommand Line and ASEP Activity
CIndicator Activity
DExecutables running from Recycle Bin
Question #31Part 1Event Search

You want to use result data from an Advanced Event Search to create a custom dashboard that displays the total number of detections during a seven-day period. Which widget allows the total number of detections to be displayed as a single numeric value?

AScatter Chart Widget
BGauge Widget
CHeat Map Widget
DTime Chart Widget
Question #32Part 1Hunting Methodology

Falcon Machine Learning prevented and quarantined a file from being written to disk, with VSCode as its parent process. The system owner compiled this file. What should the next steps be?

ADetonate the file in a private sandbox, and write a Machine Learning exclusion if the file activity is expected
BDetonate the file in a private or public sandbox, and write a Machine Learning exclusion
CDetonate the file in a private sandbox, and write an exclusion for the Indicator of Attack if the file activity is expected
Question #33Part 1Event Search

A detection includes a suspicious process namedreallysus.exe. ItsTargetProcessIdis123456789. Which query returns every event associated with this process?

ATargetProcessId=123456789 OR ContextProcessId=123456789 OR RpcClientProcessId=123456789
BTargetProcessId=123456789 OR ParentProcessId=123456789 OR RpcClientProcessId=123456789
C"#event_simpleName" = ProcessRollup2 TargetProcessId=123456789
D"#event_simpleName" = ProcessRollup2 FileName=reallysus.exe
Question #34Part 1Event Search

You need to search for every IPv4 connection made by any `powershell.exe` process. Which CQL query will help you locate these processes?

A#event__simpleName = ProcessRollup2 | FileName = "powershell.exe" | RemoteIP = "127.0.0.1"
B#event_simpleName = ProcessRollup2 | FileName = "powershell.exe" | join({#event_simpleName = NetworkConnectIP4}, field=[TargetProcessId], key=ContextProcessId)
C#event_simpleName = NetworkConnectIP4 | FileName "powershell.exe"
D#event_simpleName = NetworkConnectIP4 | join({#event_simpleName = ProcessRollup2}, field=[TargetProcessId], key=ContextProcessId)
Question #35Part 1Event Search

Your team has just received a detection about a potentially malicious binary running on an endpoint. Using CQL, you want to identify all events related to that detection. Which field is used to correlate events with this detection?

AParentProcessId
Bevent_simpleName
CComputerName
DTreeId
Question #36Part 1Event Search

Which function would you add to agroupBy()operation to display, in one record, all associated domain names with which an executable communicated?

AStats
BCollect
CBucket
DSort
Question #37Part 1Detection Analysis

You are investigating a compromise on a Linux host. You suspect the host is running an older Apache version and that the Log4j (CVE-2021-44228) vulnerability is being exploited through JNDI lookups. Which CQL query could you use to determine whether Log4j is the root cause of the compromise?

A#event_simpleName=ScriptControlDetectInfo| ScriptContent=/.* jndi:\W{1,5}:?\}?\/\/.*\}/i
B#event_simpleName=Cve-Detection| Cve-Number=CVE-2021-44228
CExternalApiType=Event_DetectionSummaryEvent| DetectDescription=/log4j/i
D#event_simpleName=HttpRequestDetectHttpRequestHeader=/.*jndi:\W{1,5}:?\}?\/\/.*\}/i
Question #38Part 1Event Search

When doesContextProcessIDhave the same value asTargetProcessID?

AWhen a process spawns a child process, the child process ID matches the TargetProcessID and the ContextProcessID of the parent
BWhen a process spawns a child process, the ContextProcessID of the child will match the TargetProcessID of the parent
CWhen a process is suspended, the TargetProcessID will match the ContextProcessID
Question #39Part 1Event Search

What is the purpose of this query? ![Question Image](https://cdn.examcademy.com/images/questions/1784139136339-z27fbgx5.png)

ADisplay all locations for local subnets on a map
BDisplay geolocation data for all network logins on a map
CDisplay all users who are logging in from private IP ranges on a map
DDisplay geolocation data for RDP connections on a map
Question #40Part 1Search and Investigation Tools

Which partial CQL query converts Unix timestamps from a web server log into a human-readable format?

A| eval(connectTime = (((requestTime/60)/60)/24)+ DATE(1970,1,1))
B| connectTime:= formatTime("%Y/%m/%d %T", field=requestTime, locale=en_US, timezone=Z)
C| connectTime:= formatTime("%Y/%m/%d %T", local=en_US, timezone=Z)
D| eval connectTime=strftime(requestTime, "%m/%d/%y %H:%M:%S")
Question #41Part 1Event Search

Which query will display file execution from a suspicious directory across all hosts?

A![](https://cdn.examcademy.com/images/questions/1785604106381-nvijdaq5.png)
B![](https://cdn.examcademy.com/images/questions/1785604108902-d9jh7zel.png)
C![](https://cdn.examcademy.com/images/questions/1785604112286-k37q37bs.png)
D![](https://cdn.examcademy.com/images/questions/1785604115492-6hkrqil7.png)
Question #42Part 1Search and Investigation Tools

Which Falcon feature provides a graphical view of users, endpoints, and the connections among them by logon type?

ARemote access graph
BGeo location activity
CHost Timeline
Question #43Part 1Event Search

You are tasked with writing a query that uses a `groupBy` statement to make data clustering easier to understand. You need to group the SHA256 value and count the unique endpoints seen. Which query will accomplish this task?

A| groupBy(SHA256HashData, function=(count(aid, distinct=true, as=uniqueEndpoints)))
B| groupBy(SHA256HashData, function=(sum(aid, distinct=true, as=uniqueEndpoints)))
C| groupBy(SHA256HashData, sum(field=aid, as=uniqueEndpoints))
D| groupBy(SHA256HashData, collect(field=aid, as=uniqueEndpoints))
Question #44Part 1Event Search

You are investigating an alert for a process that connected to the following suspicious domain:reallysuspiciousdomain[.]com. Which Investigate dashboard provides a list of processes that looked up the specified domain?

AIP addresses
BBulk domains
CGeo location activity
DRemote access graph
Question #45Part 1Hunting Analytics

You need to hunt for the least-used Windows services that start from non-standard locations. Which query below will provide this information?

A![](https://cdn.examcademy.com/images/questions/1785604119792-szjdbjc3.png)
B![](https://cdn.examcademy.com/images/questions/1785604122574-gv1hn469.png)
C![](https://cdn.examcademy.com/images/questions/1785604124984-98u0lbyv.png)
Question #46Part 1Search and Investigation Tools

You suspect that one of your hypervisors might be running a vulnerable BIOS version. Which Investigate Dashboard confirms vulnerability details, such as the type and timeline?

ABIOS Search
BBIOS Analysis
CBIOS Prevalence
DBIOS Firmware Inventory

📢 Unlock Full Access to Success!

"The content displayed here is a promotional preview and contains only 50% of the actual exam database. To access the complete set of updated questions, please upgrade to the Full Version."

👉 Click the button and follow the instructions to secure your full access immediately!